
Cybersecurity Analyst Resume Example (2026)
What makes a strong cybersecurity analyst résumé
A cybersecurity analyst resume should describe your security tasks and contribution: alert triage, investigation, remediation, access reviews or detection work. Name the SIEM, EDR tools and frameworks you actually used, with sanitized evidence that respects confidentiality. List earned credentials accurately and follow the posting’s required qualifications; Security+ and other certifications are not universal ATS filters.
Cybersecurity Analyst résumé sample
This is an illustrative résumé. Names, organizations and accomplishments are constructed examples; replace them with your own verified experience.
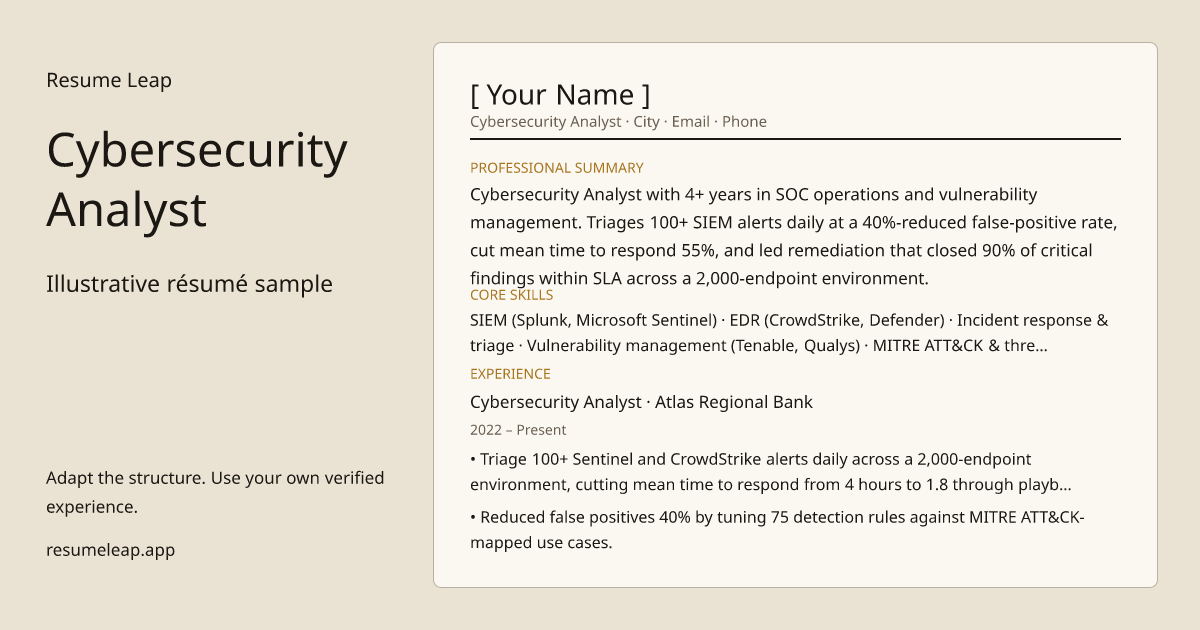
Professional Summary
Cybersecurity Analyst with 4+ years in SOC operations and vulnerability management. Triages 100+ SIEM alerts daily at a 40%-reduced false-positive rate, cut mean time to respond 55%, and led remediation that closed 90% of critical findings within SLA across a 2,000-endpoint environment.
Core Skills
Experience
- Triage 100+ Sentinel and CrowdStrike alerts daily across a 2,000-endpoint environment, cutting mean time to respond from 4 hours to 1.8 through playbook automation.
- Reduced false positives 40% by tuning 75 detection rules against MITRE ATT&CK-mapped use cases.
- Led containment on 12 confirmed incidents (BEC attempts, malware, insider misuse) with zero resulting data loss; authored post-incident reports to the CISO.
- Run the vulnerability program with Tenable: critical findings remediated within SLA rose from 60% to 90% under my ownership.
- Monitored SIEM dashboards for 30+ client environments, escalating validated threats with a 96% triage-accuracy score.
- Analyzed 200+ reported phishing emails monthly, maintaining playbooks that cut analysis time per sample 50%.
- Contributed detection content for Log4Shell response across all clients within 48 hours of disclosure.
Education
B.S. Cybersecurity — University of Maryland Global Campus
Certifications
CompTIA Security+ · CompTIA CySA+ · GIAC Security Essentials (GSEC)
Job-description terms for a cybersecurity analyst résumé
These role-related terms are prompts for reviewing a specific job description. Include only terms that accurately describe your experience. Employers use different systems and criteria; this list does not represent a universal scoring model.
More cybersecurity analyst bullet-point examples
Adapt these patterns using your own tools, scope and supported facts. Describe your action and its context, then include an outcome where you have a reliable basis for it. A useful bullet does not always need a number.
- ▸Detected and contained a business-email-compromise attempt targeting payroll within 45 minutes, preventing a fraudulent $120K transfer.
- ▸Automated phishing triage with a Python/Sentinel pipeline that cut manual analysis from 20 minutes to 4 per sample.
- ▸Cut successful phishing-simulation click rates from 18% to 6% in one year via targeted awareness training I designed.
- ▸Hardened 40 firewall rulesets during a segmentation project, reducing the externally reachable attack surface 70%.
- ▸Supported the ISO 27001 certification audit, owning 25 technical controls that passed with zero nonconformities.
- ▸Built a threat-hunting cadence (KQL, ATT&CK-based hypotheses) that surfaced two dormant persistence mechanisms missed by automated tooling.
Common cybersecurity analyst résumé mistakes
- ✕Listing security tools without incidents, detections, or remediations they produced.
- ✕Vague threat language ('protected against cyber attacks') instead of specific, sanitized incident outcomes.
- ✕Leaving relevant qualifications unclear — name credentials accurately, show their status and follow the posting’s requirements.
- ✕Naming frameworks such as NIST, MITRE ATT&CK or ISO 27001 without showing what you did with them — include only relevant, supported experience instead of assuming framework words trigger a universal screening rule.
- ✕Overclaiming severity or headline incidents — security hiring managers probe specifics and inflation is disqualifying.
Frequently asked questions
What certifications should a cybersecurity analyst resume include?
How do I quantify security work on a resume?
What can I show on a cybersecurity analyst resume without SOC experience?
Should a security resume mention specific incidents?
Build a résumé from your own experience
Create an account, add your own profile and a target job description, then use Resume Leap to draft and review your résumé. This signup link does not import the sample. Export a PDF and follow the employer’s requested format.